How to Become a GRC Analyst with CompTIA Security+: Skills, Jobs and Career Path
Cybersecurity is not limited to penetration testing, malware analysis, or configuring security tools. Organizations also need professionals who can evaluate risk, document security requirements, support audits, review policies, and explain cybersecurity issues to business leaders.
That is where governance, risk, and compliance, commonly called GRC, becomes important.
For beginners who prefer risk analysis, policy, documentation, compliance, and business-focused work, GRC can provide a practical path into cybersecurity. CompTIA Security+ may help you build the foundational security knowledge needed to understand controls, threats, access management, incident response, and risk-management concepts.
However, earning Security+ does not automatically qualify you for every GRC position or guarantee employment. Employers may also look for practical projects, familiarity with security frameworks, documentation skills, attention to detail, and the ability to communicate risk clearly.
This guide explains how to become a GRC analyst with CompTIA Security+, which skills to develop, what entry-level roles to target, and how to build a realistic career plan.
What Is a GRC Analyst?
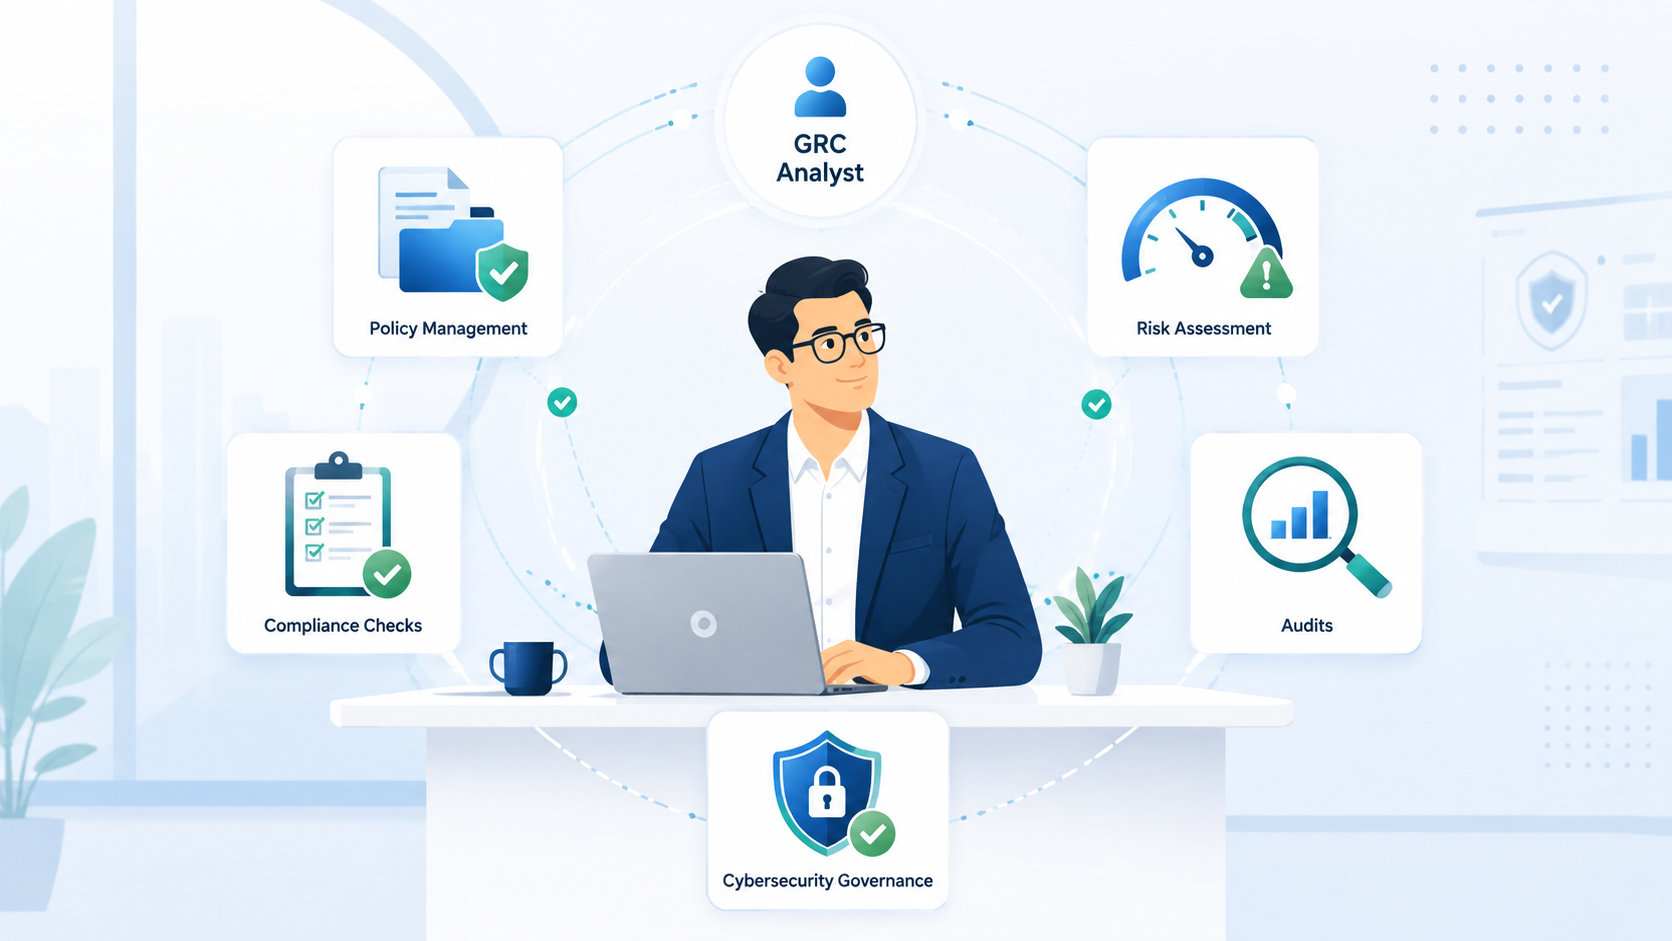
A GRC analyst helps an organization manage cybersecurity responsibilities across three connected areas:
- Governance
- Risk management
- Compliance
The exact responsibilities vary by company, industry, seniority, and regulatory environment. In one organization, a GRC analyst may focus heavily on audits. In another, the role may involve vendor assessments, policy management, security controls, or enterprise risk reporting.
Governance
Governance defines how an organization directs and oversees its cybersecurity program.
It includes:
- Security policies and standards
- Roles and responsibilities
- Management oversight
- Decision-making authority
- Accountability
- Security objectives
- Reporting processes
For example, an access-control policy may define who can approve administrative access, how access should be reviewed, and how quickly access must be removed when an employee leaves.
A GRC analyst may help review the policy, confirm that responsibilities are clear, and check whether teams are following the documented process.
Risk Management
Risk management is the process of identifying, evaluating, prioritizing, documenting, and responding to potential problems.
A cybersecurity risk usually involves:
- An important asset
- A possible threat
- A weakness or vulnerability
- A potential business impact
- Existing security controls
- Additional actions needed
A GRC analyst may record risks in a risk register, assign likelihood and impact ratings, identify the responsible owner, and track remediation activities.
Compliance
Compliance involves meeting applicable laws, regulations, contractual obligations, security standards, and internal policies.
Depending on the organization, compliance work may involve requirements connected to:
- ISO/IEC 27001
- SOC 2
- PCI DSS
- HIPAA
- GDPR
- Customer contracts
- Internal security standards
Compliance does not simply mean completing a checklist. The organization must understand which requirements apply, implement appropriate controls, collect evidence, identify gaps, and address weaknesses.
Simple GRC Risk Example
Imagine a small healthcare company stores sensitive customer data in a cloud application.
A GRC analyst discovers that several former employees still have active accounts.
The analyst may:
- Identify unauthorized access as a security risk.
- Review the existing employee offboarding control.
- Document that account removal is not completed consistently.
- Rate the likelihood and impact of the risk.
- Recommend an automated account-deactivation process.
- Assign an owner and remediation deadline.
- Track the issue until the control is implemented.
This example combines governance, risk management, compliance, documentation, and communication.
What Does a GRC Analyst Do?
A GRC analyst’s daily work may include:
- Reviewing and updating security policies
- Supporting cybersecurity risk assessments
- Maintaining risk registers
- Collecting evidence for internal or external audits
- Evaluating whether security controls are working
- Documenting compliance gaps
- Tracking remediation activities
- Reviewing third-party vendors
- Supporting security-awareness initiatives
- Preparing reports for management
- Coordinating with auditors and technical teams
- Explaining risk to nontechnical stakeholders
A GRC analyst may ask a system administrator for screenshots showing access settings, request training records from human resources, review vendor security documents, or prepare a summary for senior management.
The role requires more than technical knowledge. Strong analysts must be organized, accurate, curious, and comfortable working with people across different departments.
Can CompTIA Security+ Help You Become a GRC Analyst?
Yes, CompTIA Security+ can support a beginner’s transition into GRC by providing a broad foundation in cybersecurity.
Security+ introduces concepts related to:
- Security controls
- Threats and vulnerabilities
- Risk management
- Policies and procedures
- Identity and access management
- Incident response
- Data protection
- Security architecture
- Security program oversight
These topics are relevant because GRC professionals must understand what security controls are intended to accomplish and why specific risks matter.
For example, when reviewing an access-control process, you need to understand authentication, authorization, least privilege, account management, and privileged access. When reviewing incident-response documentation, you should understand the purpose of preparation, detection, containment, recovery, and reporting.
Security+ may also demonstrate that you have invested time in learning cybersecurity fundamentals. However, it has important limitations.
The certification does not replace:
- Professional experience
- Framework knowledge
- Audit-support skills
- Policy-writing ability
- Risk-assessment practice
- Evidence collection
- Business communication
- Practical documentation experience
The strongest approach is to combine Security+ with hands-on GRC projects and targeted job preparation.
How to Become a GRC Analyst with CompTIA Security+
The following roadmap can help you move from beginner-level cybersecurity study to entry-level GRC applications.
Step 1: Learn Cybersecurity Fundamentals
Before specializing in GRC, build a working understanding of:
- Networks and common protocols
- Authentication and access control
- Threats and vulnerabilities
- Security controls
- Cloud computing
- Data protection
- Incident response
- Security policies
- Risk terminology
You do not need to become an expert engineer. However, you should understand enough technical context to evaluate risks and communicate with security, IT, cloud, and development teams.
Step 2: Prepare for CompTIA Security+
Use the official exam objectives to organize your study plan. Avoid relying entirely on passive video watching or memorizing isolated definitions.
A balanced study process may include:
- Structured training
- Written notes
- Regular review sessions
- Flashcards for important terms
- Scenario-based questions
- Practice exams
- Explanations for incorrect answers
- Additional study of weak domains
When reviewing a practice question, focus on why one answer is appropriate and why the alternatives are less suitable.
No training course or practice test can guarantee that you will pass. Practice exams should help you identify knowledge gaps and become familiar with applying concepts in realistic scenarios.
Step 3: Learn Common GRC Frameworks
Security frameworks provide structured ways to organize controls, manage risks, and evaluate security programs.
Useful frameworks and standards include:
- NIST Cybersecurity Framework
- NIST Risk Management Framework
- ISO/IEC 27001
- CIS Controls
- SOC 2
- PCI DSS
- HIPAA
- GDPR
You do not need to master all of them immediately.
Begin with one broad framework, such as the NIST Cybersecurity Framework, and learn how it organizes security activities. You can then explore requirements connected to your target industry.
For example, healthcare roles may involve privacy and healthcare-related requirements, while payment-processing organizations may focus more heavily on PCI DSS.
Step 4: Develop Practical GRC Skills
Employers are more likely to understand your capabilities when you can show completed work.
Practise activities such as:
- Writing a basic security policy
- Creating a risk register
- Performing a simple risk assessment
- Mapping controls to framework requirements
- Preparing an evidence-request list
- Reviewing a fictional vendor
- Recording compliance findings
- Writing remediation recommendations
Use fictional organizations and clearly label the work as a personal project. Do not present practice exercises as professional experience.
Step 5: Build Business and Communication Skills
GRC professionals regularly communicate with:
- Managers
- Auditors
- Security engineers
- IT administrators
- Vendors
- Legal or privacy teams
- Human resources
- Business leaders
A technical risk must often be translated into business impact.
Instead of saying, “The server uses an unsupported protocol,” a GRC analyst may explain:
The outdated protocol increases the possibility of unauthorized access to customer information, which could interrupt operations and create compliance concerns.
Clear communication helps decision-makers understand why remediation deserves time, budget, or management attention.
Step 6: Create a GRC-Focused Resume
Your resume should connect your existing experience to GRC responsibilities.
Relevant transferable experience may include:
- Writing procedures
- Handling sensitive information
- Reviewing records
- Supporting quality checks
- Managing tickets
- Coordinating projects
- Creating reports
- Following regulated processes
- Communicating with customers or vendors
Include Security+, framework study, and personal projects without exaggerating your experience.
Sample resume bullet:
- Created a fictional cybersecurity risk register covering 12 business risks, assigned likelihood and impact ratings, mapped recommended controls to the NIST Cybersecurity Framework, and prepared a management summary.
This bullet describes a real project without implying that it was completed for an employer.
Step 7: Apply for Entry-Level GRC Jobs
Do not search only for positions containing “GRC” in the title. Employers use many titles for similar work.
Read job descriptions carefully and identify repeated responsibilities, such as:
- Risk assessments
- Evidence collection
- Control testing
- Policy review
- Vendor assessments
- Compliance monitoring
- Audit support
- Remediation tracking
Apply when you meet the core responsibilities, even when you do not satisfy every preferred qualification. Preferred requirements often describe an employer’s strongest possible candidate rather than the only person who may be considered.
Essential GRC Analyst Skills
Cybersecurity and Technical Foundations
A GRC analyst should understand:
- Security controls
- Network fundamentals
- Identity and access management
- Vulnerability management
- Incident response
- Cloud concepts
- Data classification
- Encryption
- Backup and recovery
- System administration basics
You may not configure every control yourself, but you should understand its purpose and the risk it is intended to reduce.
Risk and Compliance Skills
Important risk and compliance abilities include:
- Identifying risks
- Evaluating likelihood and impact
- Reviewing controls
- Performing gap analysis
- Supporting audits
- Collecting evidence
- Tracking remediation
- Understanding regulatory requirements
- Reviewing third-party vendors
- Maintaining risk records
A strong analyst does not simply identify a weakness. The analyst explains its impact, recommends a practical response, and tracks the issue.
Documentation Skills
GRC work produces substantial documentation, including:
- Policies
- Procedures
- Risk registers
- Control matrices
- Audit records
- Assessment reports
- Evidence inventories
- Remediation plans
- Vendor reviews
- Management summaries
Documents must be accurate, understandable, current, and easy to review.
Communication and Business Skills
GRC analysts also need:
- Critical thinking
- Attention to detail
- Organization
- Time management
- Stakeholder communication
- Presentation skills
- Project coordination
- Professional writing
- Interviewing skills
- Business-impact analysis
The ability to explain a complicated risk clearly can be as important as identifying it.
Entry-Level GRC Jobs to Consider
Employers may use different titles for positions with overlapping responsibilities.
Junior GRC Analyst
Supports risk assessments, policy reviews, evidence collection, control documentation, and remediation tracking.
Security+ knowledge may help you understand the technical controls being evaluated.
Cybersecurity Compliance Analyst
Focuses on compliance requirements, control reviews, evidence gathering, gap documentation, and assessment support.
IT Risk Analyst
Identifies technology risks, maintains risk records, works with risk owners, and tracks risk-treatment decisions.
Information Security Analyst
This broad title may include operational security, risk, policy, compliance, or control-review responsibilities. Read the job description carefully.
Third-Party Risk Analyst
Reviews the security practices of vendors and service providers through questionnaires, documentation, contracts, and risk assessments.
Security Controls Analyst
Evaluates whether controls are documented, implemented, and operating as expected.
IT Audit Associate
Supports audit planning, evidence collection, interviews, testing, documentation, and reporting.
Governance Analyst
Helps maintain policies, standards, responsibilities, security committees, reporting processes, and program documentation.
Privacy or Compliance Coordinator
Supports privacy records, regulatory processes, training documentation, evidence collection, and compliance activities.
Security+ may be relevant to these positions, but it is not a universal requirement. Each employer determines its own qualifications.
Industries That Hire GRC Professionals
GRC responsibilities appear in many industries because organizations must protect information, manage operational risks, and meet contractual or regulatory obligations.
Financial Services
Banks, payment providers, and insurance companies manage sensitive financial information and must maintain strong controls, risk oversight, and audit records.
Healthcare
Healthcare organizations must protect sensitive patient and business information while supporting privacy, access-control, and risk-management requirements.
Government
Government agencies and contractors often operate under formal security requirements and detailed documentation processes.
Technology and Cloud Services
Technology companies must manage product security, customer expectations, vendor risk, access controls, incident response, and assurance programs.
Consulting
Consulting organizations may help clients conduct risk assessments, prepare for audits, review controls, and improve security programs.
Retail and E-Commerce
Retailers manage payment information, customer accounts, online platforms, vendors, and fraud-related risks.
Telecommunications
Telecommunications organizations manage large networks, customer data, service availability, and third-party relationships.
Education
Schools and universities handle student information, research data, payment records, cloud systems, and access-control risks.
Critical Infrastructure
Energy, transportation, utilities, and similar sectors must manage cybersecurity risks that may affect essential services.
GRC Analyst Career Path
A possible GRC analyst career path may progress through the following stages:
- IT support, security support, audit support, or compliance coordinator
- Junior GRC analyst or IT risk analyst
- GRC analyst or cybersecurity compliance analyst
- Senior GRC analyst, security governance specialist, or risk manager
- GRC manager, information security manager, consultant, or security leader
This path is not universal.
Someone with audit experience may move directly into compliance. An IT support professional may transition into security controls. A project coordinator may enter vendor risk or governance. Career progression depends on your experience, location, employer, industry, and professional goals.
Certifications to Consider After CompTIA Security+
Additional certifications are not mandatory, but they may support specialized career goals.
After gaining foundational knowledge and practical experience, you may consider credentials related to:
- Advanced cybersecurity
- Information systems auditing
- Governance and risk management
- Privacy
- Cloud security
- ISO/IEC 27001
- Regulatory compliance
- Third-party risk
- Security management
Choose a certification based on the responsibilities of your target role. Avoid collecting credentials without building practical skills.
For example, an audit-focused professional may choose a different path from someone specializing in privacy, cloud compliance, or enterprise risk.
Practical GRC Portfolio Project for Beginners
Create a fictional company called BrightPath Services, a 40-person business that stores customer records in cloud applications and allows employees to work remotely.
Project Tasks
1. Identify Important Assets
List assets such as:
- Customer records
- Employee information
- Email accounts
- Cloud storage
- Laptops
- Financial records
- Business applications
2. Identify Cybersecurity Risks
Document risks such as:
- Former employees retaining access
- Weak passwords
- Missing multifactor authentication
- Unencrypted laptops
- Incomplete backups
- Excessive administrator privileges
- Vendor access not being reviewed
- Employees receiving phishing emails
3. Assign Ratings
Give each risk a likelihood and impact rating, such as low, medium, or high.
Explain your reasoning in one or two sentences.
4. Build a Risk Register
Include columns for:
- Risk ID
- Asset
- Threat
- Vulnerability
- Existing control
- Likelihood
- Impact
- Overall rating
- Recommended action
- Risk owner
- Target date
- Status
5. Recommend Controls
Examples include:
- Multifactor authentication
- Quarterly access reviews
- Employee offboarding checklists
- Security-awareness training
- Laptop encryption
- Tested backups
- Vendor-access expiration
- Privileged-access restrictions
6. Map Controls to a Framework
Choose a recognized framework and show how selected controls support relevant functions or requirements.
You do not need to map every control. A small, accurate mapping is more useful than a large but unclear spreadsheet.
7. Write a One-Page Security Policy
Create a short access-control policy covering:
- Account approval
- Password expectations
- Multifactor authentication
- Privileged access
- Access reviews
- Employee termination
- Policy exceptions
8. Prepare a Management Summary
Write a one-page summary explaining:
- The most important risks
- Their potential business impact
- Recommended priorities
- Suggested next steps
During an interview, you can discuss your risk register, policy, framework mapping, and management summary. Explain your decisions and what you learned from the project.
Common Mistakes to Avoid
Collecting Certifications Without Building Skills
Certifications can support learning, but they should be combined with projects, documentation practice, and applied scenarios.
Ignoring Communication and Documentation
GRC work depends heavily on clear writing, accurate records, and stakeholder coordination. Practise explaining risks without unnecessary jargon.
Trying to Learn Every Framework at Once
Start with one foundational framework. Expand based on the industries and jobs you are targeting.
Applying Only to Roles With “GRC” in the Title
Search for compliance, IT risk, controls, audit, governance, privacy, assurance, and vendor-risk positions.
Claiming Experience You Do Not Have
Describe personal projects honestly. Never present fictional or classroom work as paid professional experience.
Memorizing Definitions Without Understanding Impact
Ask how each concept affects operations, customers, finances, legal obligations, or business objectives.
Assuming Security+ Guarantees a Job
Security+ can strengthen your foundation, but employers may also evaluate your projects, communication abilities, experience, framework knowledge, and interview performance.
A 90-Day Beginner GRC Career Plan
Days 1–30: Build the Foundation
During the first month:
- Study cybersecurity fundamentals
- Begin structured Security+ preparation
- Learn basic governance, risk, and compliance terminology
- Review security controls and access-management concepts
- Read an introductory overview of the NIST Cybersecurity Framework
- Create a weekly study schedule
- Record unfamiliar terms and review them regularly
Focus on consistency rather than trying to study everything at once.
Days 31–60: Develop Practical Skills
During the second month:
- Create a fictional company
- Build a basic risk register
- Perform a simple risk assessment
- Map selected controls to a framework
- Write a one-page security policy
- Prepare an audit-evidence checklist
- Complete a fictional vendor-risk review
- Continue Security+ study and practice questions
By the end of this phase, you should have several portfolio materials that demonstrate your thought process.
Days 61–90: Prepare for Employment
During the final month:
- Update your resume
- Improve your LinkedIn profile
- Add an honest project section
- Prepare explanations of your portfolio work
- Practise common GRC interview questions
- Review Security+ weak areas
- Complete realistic practice exams
- Connect with cybersecurity and compliance professionals
- Identify target employers
- Apply for relevant entry-level positions
For part-time learners, the goal is not to become an expert in 90 days. The goal is to build a stronger foundation, produce practical work, and begin making targeted applications.
Frequently Asked Questions
Is CompTIA Security+ good for GRC jobs?
Security+ can provide useful cybersecurity knowledge for GRC roles, especially in areas such as risk, controls, policies, access management, and incident response. It does not guarantee employment and should be combined with practical GRC skills.
Can I become a GRC analyst without cybersecurity experience?
Yes, some people enter GRC from IT support, auditing, quality assurance, privacy, project coordination, legal operations, or compliance. Transferable skills and portfolio projects can help demonstrate your potential.
Do GRC analysts need coding skills?
Coding is not required for every GRC role. Basic scripting or data-analysis skills may be useful, but documentation, risk analysis, communication, and control knowledge are often more central.
What entry-level GRC jobs can I apply for?
Possible roles include junior GRC analyst, IT risk analyst, compliance analyst, third-party risk analyst, IT audit associate, security controls analyst, governance analyst, and privacy coordinator.
Is GRC less technical than other cybersecurity fields?
GRC is often less hands-on than penetration testing or security engineering, but it still requires technical understanding. Analysts must understand systems, controls, vulnerabilities, and business risks.
Which frameworks should a beginner learn first?
A broad framework such as the NIST Cybersecurity Framework can provide a useful starting point. The next framework should depend on your target role and industry.
Can Security+ help with a cybersecurity compliance career?
Yes. Security+ can help you understand the security concepts behind many compliance requirements. You will still need to learn how controls are documented, assessed, and supported with evidence.
What practical projects can I add to a GRC portfolio?
You can create a risk register, security policy, vendor-risk assessment, control matrix, audit-evidence checklist, remediation plan, or management risk summary for a fictional company.
How long does it take to become a GRC analyst?
There is no fixed timeline. It depends on your previous experience, study schedule, local job market, practical skills, and the positions you target.
What should I study after CompTIA Security+?
Study the frameworks and responsibilities connected to your target role. You may later explore auditing, privacy, cloud security, risk management, governance, or advanced cybersecurity credentials.
Conclusion
Learning how to become a GRC analyst with CompTIA Security+ involves more than passing one certification exam.
Security+ can help you build a useful cybersecurity foundation, but a competitive beginner should also develop:
- Practical risk-assessment skills
- Framework knowledge
- Policy and documentation abilities
- Control-assessment experience
- Business communication
- A realistic GRC portfolio
- A targeted job-search strategy
You do not need to master every framework or qualify for every GRC position before applying. Start with the fundamentals, build one practical project, document your work honestly, and improve your skills as you gain experience.
Final Call to Action
Begin your CompTIA Security+ preparation with structured training, consistent review, and realistic practice questions that require you to apply cybersecurity concepts—not simply memorize definitions.
As you study, connect each topic to a GRC responsibility. Ask how a control reduces risk, what evidence could demonstrate that it is working, and how you would explain its importance to a business leader.
That approach can help you prepare for the certification while building the analytical mindset needed for a cybersecurity compliance career.